Features
Security and roles
Roles and permissions per complex, a verifiable audit log, encryption and isolated organizations.
Partly available
Access follows the association’s real structure: a role is always held in one organization or one complex, and every request is checked against it. What HOA Portal cannot let you see, it does not show at all.
What it does
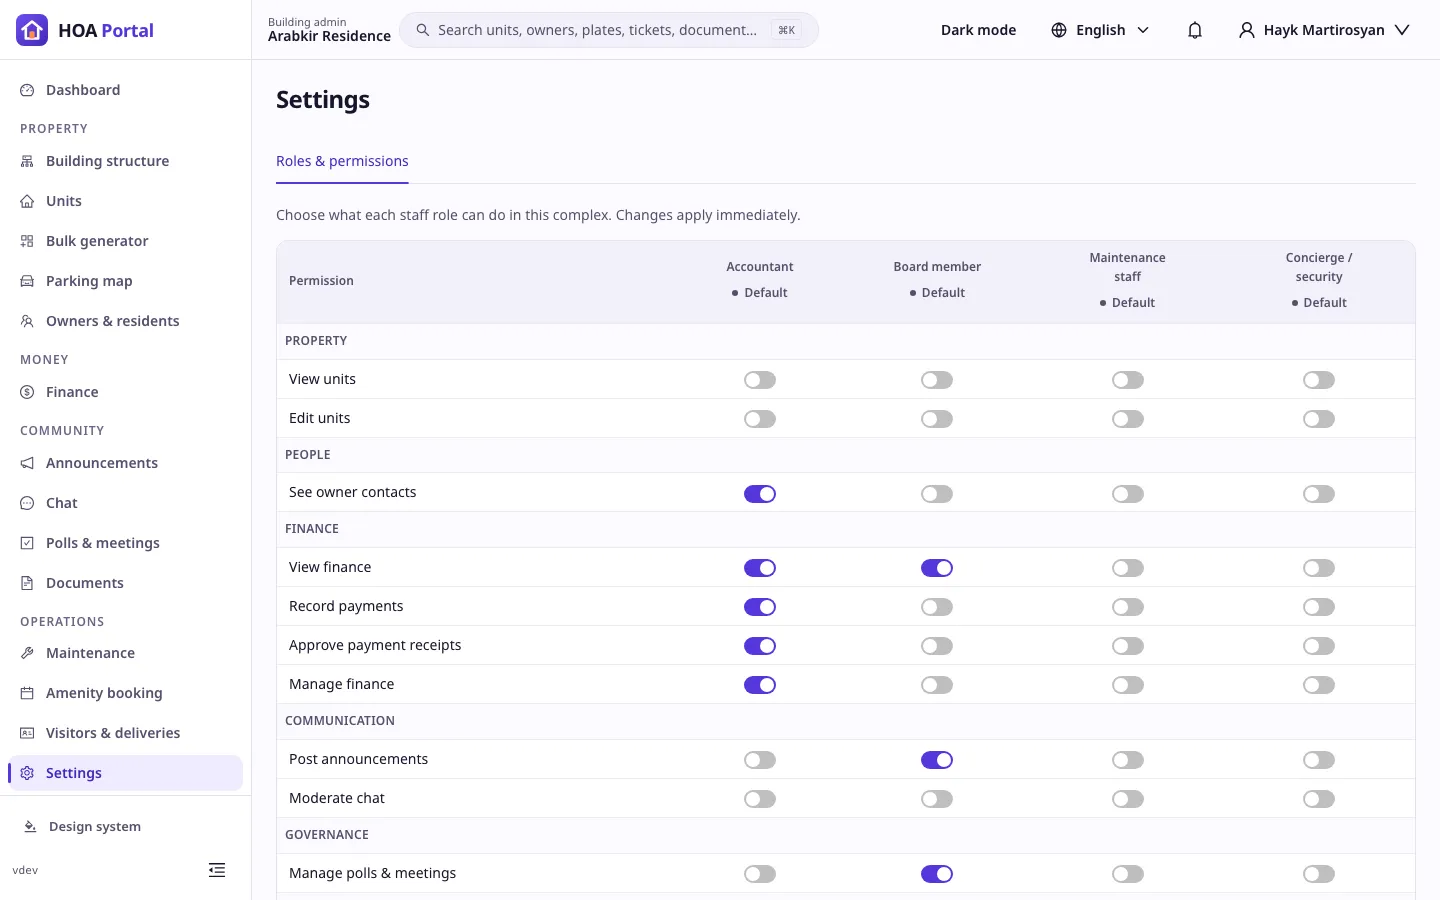
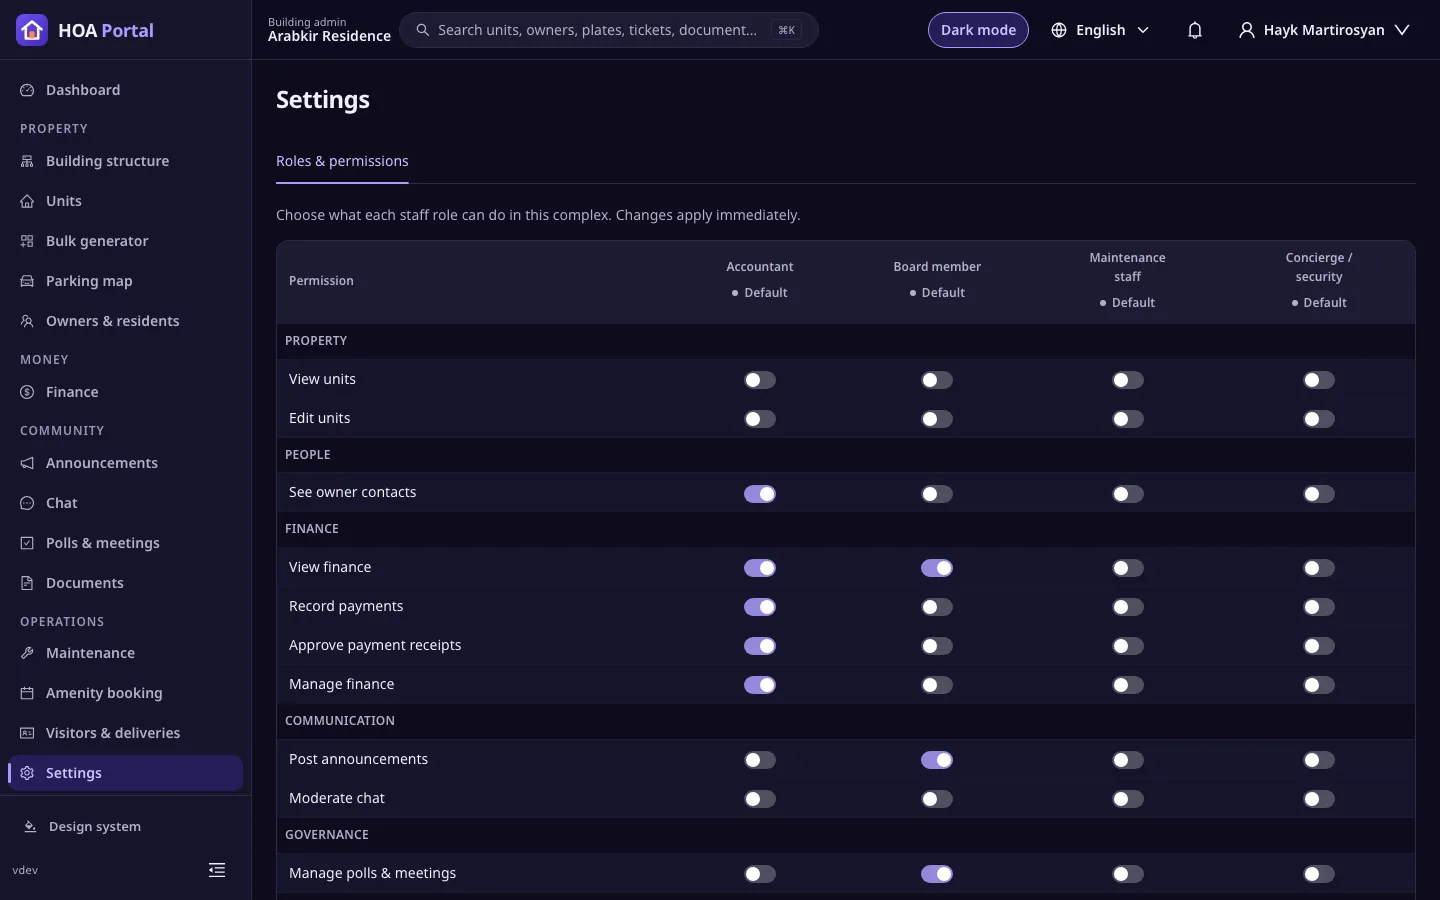
Roles and permissions
AvailableOrg and complex admins, accountants, board members, maintenance staff, concierges, owners and residents — each role's permissions can be tuned per complex.
One account, many roles
AvailableThe same person can manage one complex and own a flat in another, and switches between them in the header.
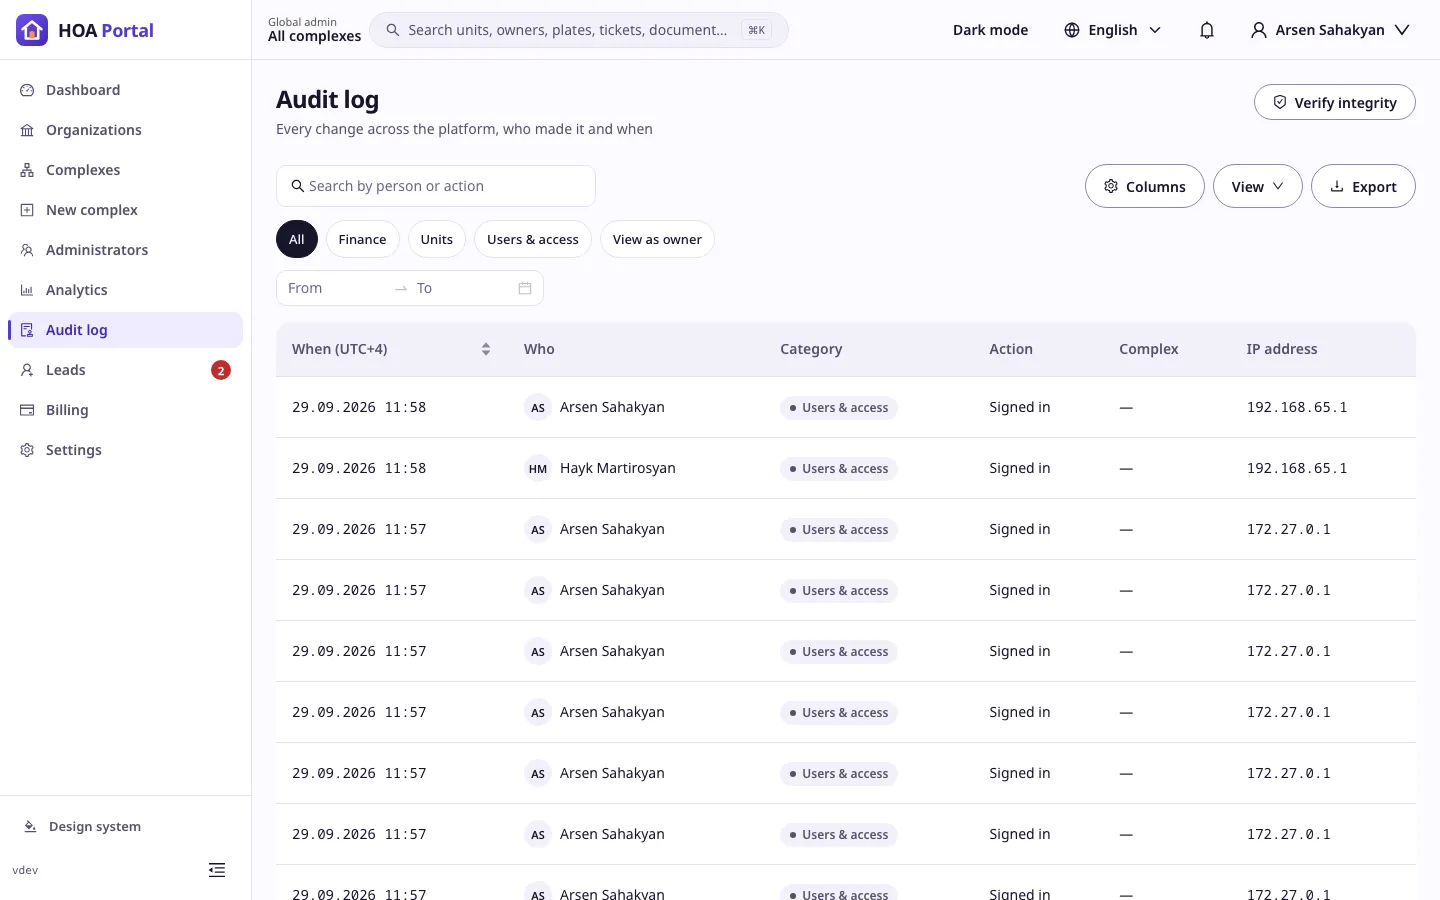
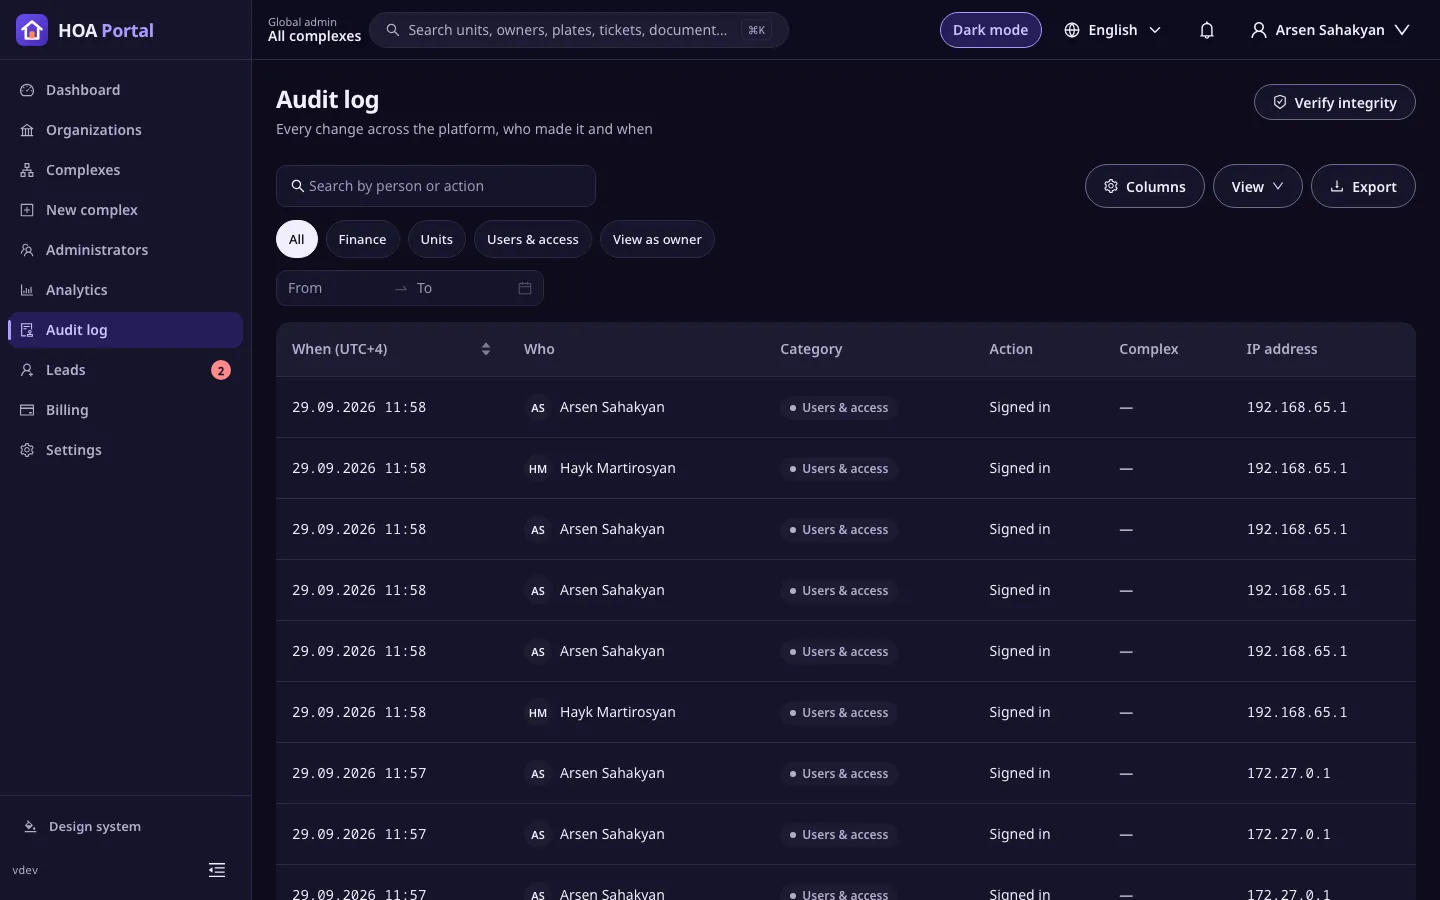
Verifiable audit log
AvailableSecurity-relevant actions are written to an append-only log chained with HMAC, and a check proves nothing was changed.
Isolated organizations
AvailableEach management company's data is kept apart; outside your scope, a record simply does not exist for you.
Encryption and secure sessions
AvailableSecrets are encrypted with AES-256-GCM, sign-in tokens are short-lived and every device has its own session.
Invitations
AvailablePeople join by invitation for a fixed role and scope; nobody can grant a role to themselves or beyond their own scope.
View as owner
Coming soonAdmins can see an owner's view to help them — read-only, and every view is audited.
In the app
Try the parts that are ready
Roles and permissions, the audit log and exports already work; the rest follows phase by phase.